
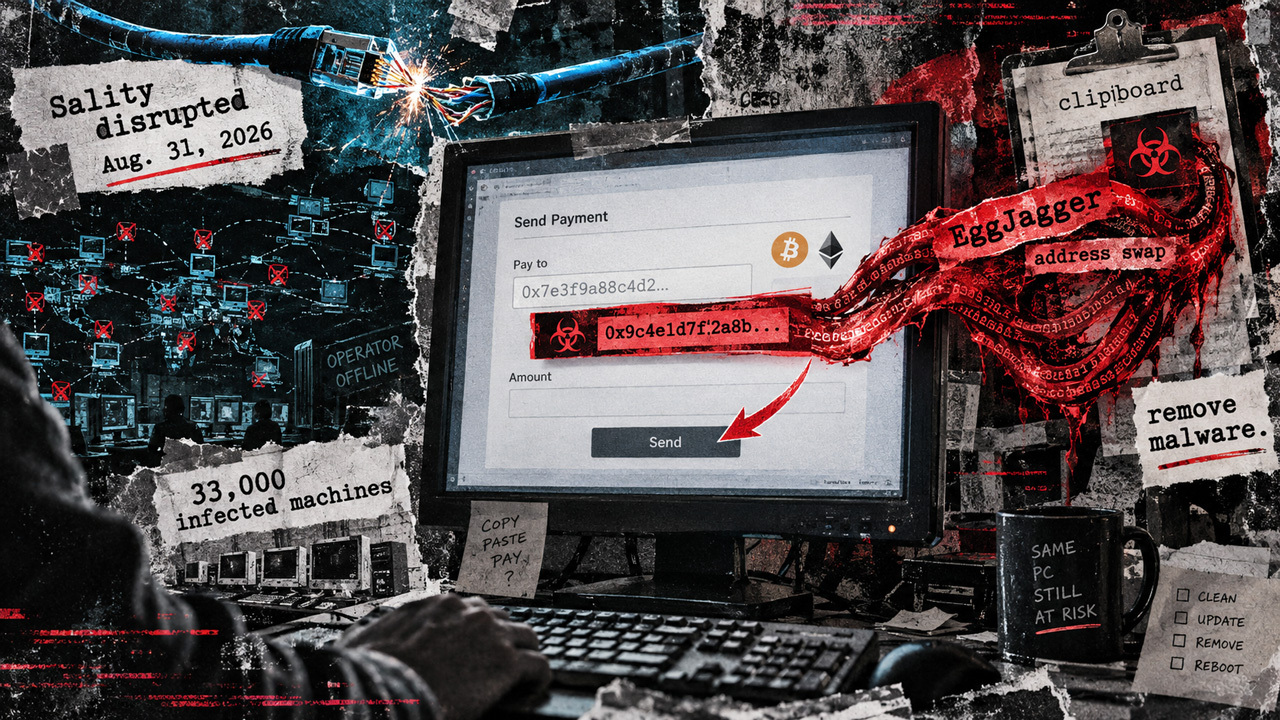
CrowdStrike says a disruption on Aug. 31 stopped hackers from delivering new malware payloads, but users with previously installed malware may remain exposed to cryptocurrency address substitution. The malicious software can monitor copied wallet addresses and replace them with an attacker-controlled address before a payment is completed, creating a “copy and paste” risk for crypto users. The warning means the disruption did not remove malware already present on affected devices. Crypto payments sent to a substituted address could therefore be redirected even after the hackers’ ability to distribute additional payloads was cut off. CryptoSlate reported the development on Sept. 8, citing CrowdStrike’s assessment. The information is relevant to users handling assets including CRO, DEL, ENS, RED and TAC, although the supplied report does not identify any specific token, wallet or transaction as affected.




