Fake Claude App Distributes Malware Targeting Crypto Wallets
Cointelegraph reports that a fake Claude desktop app is distributing RevStealer malware, which targets more than 50 crypto wallets and can collect browser credentials, cookies, messaging data and selected documents.
Cointelegraph
2 unique views

A counterfeit desktop application presented as Claude is being used to distribute RevStealer malware, according to Cointelegraph. The malware targets more than 50 cryptocurrency wallets and can also collect browser passwords, cookies, messaging data and selected documents. The report highlights a security risk for crypto users who download desktop software from unverified sources. The affected assets listed in connection with the report include AKE, DATA, ONG, ORE, ALE and WAL. No information was provided on financial losses, the number of affected users or any impact on the prices of those tokens. The report was published on September 1, 2026.
Source
Cointelegraph
This is an original Moneyiar brief based on the cited source.
Read original source ↗
Related news
Based on this story’s market and assets
Bitcoin Core 32 Moves Into Final Testing With Validation and Security Updates
Bitcoin Core 32 has entered final testing ahead of its October update, which will bring faster validation, changes to fee estimation and block processing, plus a security fix for a wallet flaw.
CoinDesk
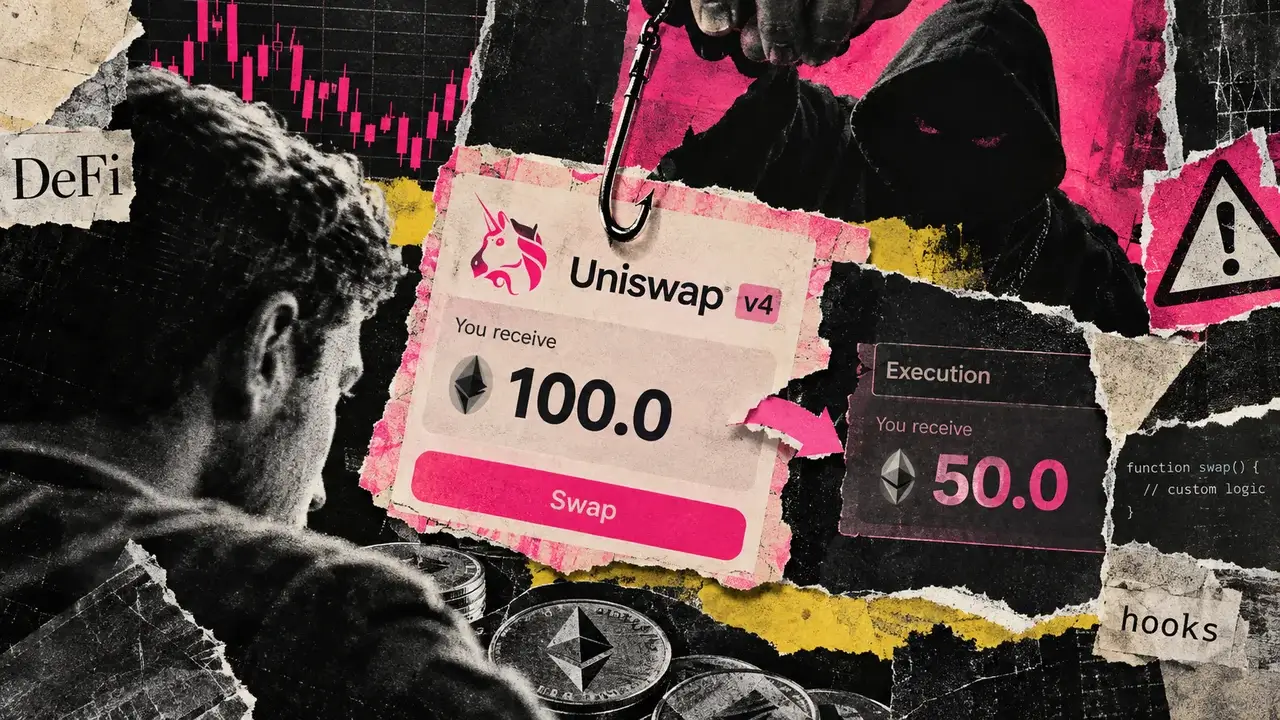
Fake Uniswap v4 Quotes May Mislead DeFi Traders
Malicious Uniswap v4 hooks can display attractive quotes to win aggregator routing, then alter their behavior when trades settle. The tactic may leave DeFi traders with execution different from the price initially presented.
CryptoSlate