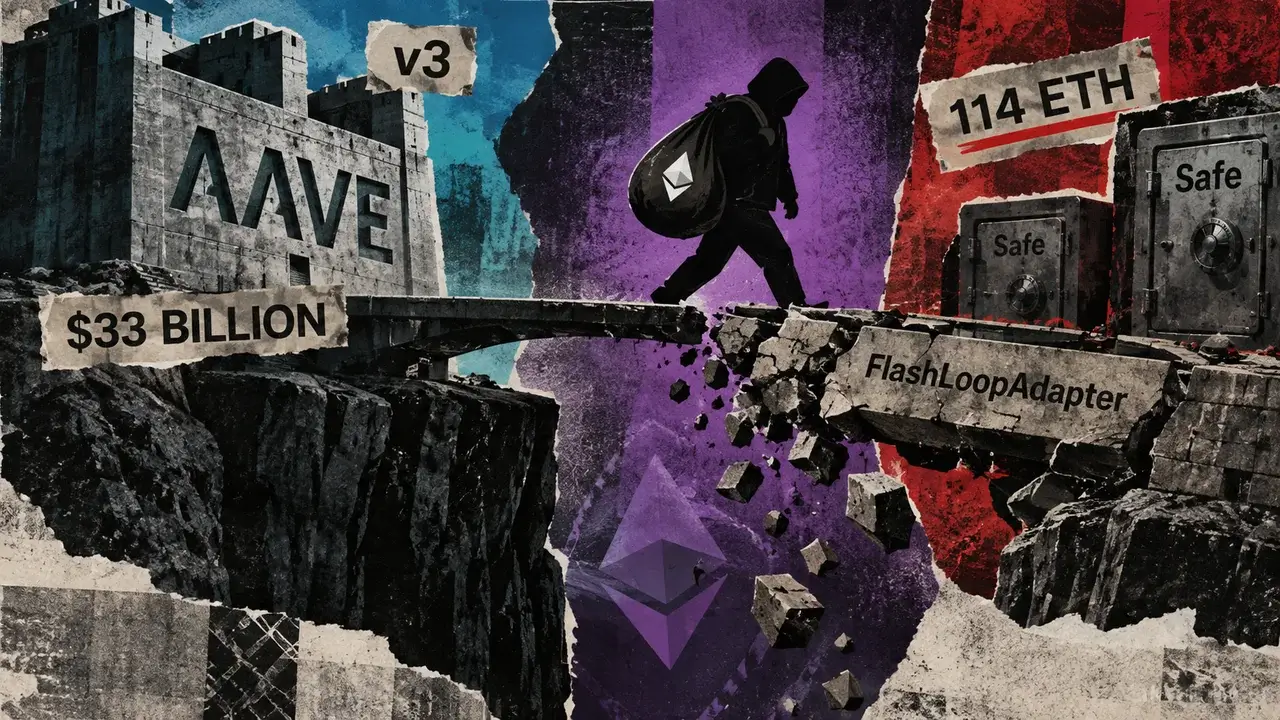
A vulnerability in a third-party adapter used with Aave v3 allowed an attacker to remove about 114 ETH in collateral from two Safe multisig wallets, according to CryptoSlate. The incident did not compromise Aave v3’s core smart contracts, but it has drawn attention to the additional risks created by external tools connected to major decentralised-finance protocols.
Attack targeted infrastructure around Aave
Blockchain security firm SlowMist said on Oct. 2 that the attacker exploited the FlashLoopAdapter, an external lending tool built to work with Aave v3 positions. The direct loss was estimated at about 114.09 ETH, worth more than $300,000 based on the report’s valuation.
The affected funds were held through two Safe multisig wallets. Safe wallets require multiple authorised parties or accounts to approve transactions, but the adapter’s weaknesses gave the attacker a route to execute actions through the wallets.
SlowMist also reported that approximately 1,300 WETH of debt was repaid during the incident. WETH, or wrapped Ether, is a token designed to represent ETH in applications that use token-based smart-contract standards. Repaying the debt released collateral connected to the affected Aave positions, allowing the attacker to withdraw assets including weETH and other collateral.
Aave founder Stani Kulechov said the exploit did not involve the lending protocol’s core contracts. “This is not Aave v3 contract, it’s third party external adapter built on top of Aave, zero effect on Aave v3,” he said.
That distinction matters because Aave is the underlying decentralised lending protocol, while the FlashLoopAdapter was an additional piece of software interacting with it. Aave’s core contracts can remain unaffected even when a connected application or adapter is compromised.
How the authentication flaw worked
SlowMist traced the problem to the adapter’s open() and close() functions. These functions checked whether the Safe calling them had enabled the FlashLoopAdapter as a module, effectively serving as an authorisation test.
The security firm said that check could be falsified. The attacker deployed a fake Safe contract programmed to return a positive response when asked whether the adapter had been enabled. The FlashLoopAdapter accepted that response as valid and continued into its internal swap process.
A second design weakness made the bypass more serious. The adapter allowed the caller to choose both the router for an external transaction and the calldata—the encoded instructions describing what that transaction should do.
The attacker directed the router back to the victim Safe and supplied instructions calling Safe’s execTransactionFromModule function. Since the FlashLoopAdapter was already enabled as a module on the targeted wallets, the call created a way to execute transactions through those Safes.
Using that route, the attacker withdrew weETH and collateral linked to Aave positions. The sequence shows how an authentication weakness in an auxiliary application can become a direct route to assets held in a wallet, even when the main lending protocol has not been breached.
Exposure now depends on adapter use
The immediate impact appears limited to users who had enabled the vulnerable module, rather than to all Aave users. However, investigators still need to determine how broadly the FlashLoopAdapter had been deployed and whether other wallets or positions remain exposed.
The incident also illustrates a wider challenge in decentralised finance. Users often interact with protocols through adapters, automated strategies, wallet modules and other integrations. Each additional component can introduce its own code, permissions and authentication logic. As a result, protecting the core protocol does not automatically protect every tool connected to it.
The outstanding questions are whether other Safe wallets enabled the same adapter and whether the developers can identify further affected positions before the same flaw is reused. The available information did not establish that Aave v3’s core contracts or all Aave positions were at risk.
Aave has more than $33 billion in total value locked, according to the source material. That scale makes the separation between the protocol itself and third-party infrastructure especially important when assessing the scope of an incident.
Current market picture
Moneyiar market data recorded on Oct. 3, 2026, at 09:39 +03:30 showed ETH at $2,682.79, down 2.39% over 24 hours and up 0.07% over seven days. AAVE was trading at $180.48, down 1.27% over 24 hours but up 17.97% over seven days.
For comparison, ADA stood at $0.2436, down 4.81% over 24 hours and 4.12% over seven days. APT was $0.7865, down 5.18% over 24 hours and 6.61% over seven days. These figures are Moneyiar data at the stated time and describe market movements, not the financial impact of the exploit itself.